AI reads sensitive data.
California wants proof.

Protecto masks sensitive personal information before it reaches models, agents and logs, on your servers or as SaaS, and records each step for your CCPA risk assessment.
Risk assessment · CopilotIllustrative
Purpose
Summarize support tickets for agents
Sensitive data
Card + codeDiagnosisHome address
Model receives
Tokens only
[CARD_9b2][PERSON_4e7]
Safeguards
Masking before the model, unmasking by role
Evidence
Protecto log for each request
Fields from 11 CCR 7152(a)
Trusted by regulated enterprises & agentic platforms
Inovalon
Automation Anywhere
Citrix
Bank Of Muscat Logo
Dell
Case study result
In production at Automation Anywhere
5,000+
Live tenants at Automation Anywhere
Policy
Set by each tenant
Higher F1
Than AWS Comprehend and Microsoft Presidio in a UT Dallas benchmark
The problem

The AI workflow is live. The risk assessment is not.

A support agent asks the AI assistant to summarize a ticket. The customer pasted a card number and code, and named a diagnosis. All of it reaches the model.
The need

AI on tickets, chats and accounts

Support tickets, chat transcripts, claims notes and account records are where AI saves the most time. Customers type sensitive details into all of them.
The challenge

Sensitive data now needs a risk assessment

Since January 1, 2026, the CCPA rules treat processing sensitive personal information as a significant risk. You assess it in writing before the processing starts.
The gap

Privacy tools stop at the website

Cookie banners and opt-out links control collection. They do not see what reaches the model, the embeddings or the vendor’s logs. California counts AI systems that can output personal information as personal information.
The risk

An executive signs the result

Workflows that were running before 2026 need a documented assessment by December 31, 2027. An executive attests to the submission under penalty of perjury by April 1, 2028.
Sensitive under the CCPASSN, driver's license, passportCard or account number with codePrecise geolocationHealthEmail and text contentsRacial or ethnic originBiometric, genetic, neural data
How it works

One checkpoint before the model, the index and the logs.

Protecto sits between your AI workflows and everything downstream. Models, vector stores and logs get tokens. Real values go only to roles your policy names, with a log.
Real timeProtects model input, retrieval, logs, MCP tool calls, and agent memory as data moves, not just stored files.
Architecture: support tickets, CRM and account records, claims and care notes, and agent context pass through Protecto. Protecto detects sensitive personal information, tokenizes it, applies a policy per recipient and logs every decision, which feeds the evidence for a CCPA risk assessment. Vector stores, logs and AI model providers receive tokens. Billing and fraud tools and named roles receive real values by policy, and each release is logged.Your systems · Protecto on-premises, in private cloud or as SaaSModel providers · their cloudCalifornia customer dataTickets and chatsFree textCRM and accountsCards, SSNs, addressesClaims, care notesHealth detailsAgent contextMemory, tool resultsProtectoOne checkpoint for every AI flow1DetectSSNs, cards, health, location2TokenizeConsistent, format-preserving3Apply policyA rule per model, tool, role4LogEvery decision, recordedToken vault: mappings kept apartRisk assessment evidenceWhat each recipient received, andwho saw real values (§7152 safeguards).Vector store (RAG)TokensLogs and monitoringTokensBilling, fraud toolsCard, loggedPeople by roleUnmask by roleTokens onlyAI modelsAny providerOpenAIAnthropicGooglexAIOr a model you host,for example with OllamaSees tokens onlyAnswers come back with tokens.Protecto restores real values only forthe tools and people your policy names.Dana Whitley[PERSON_4e7]4111 …1111[CARD_9b2]4111 …1111[PERSON_4e7]Architecture: support tickets, CRM and account records, claims and care notes, and agent context pass through Protecto. Protecto detects sensitive personal information, tokenizes it, applies a policy per recipient and logs every decision, which feeds the evidence for a CCPA risk assessment. Vector stores, logs and AI model providers receive tokens. Billing and fraud tools and named roles receive real values by policy, and each release is logged.Your systemsProtecto on-prem, private cloud or SaaSTickets, chatsCRM, accountsClaims notesAgent contextProtecto1DetectSSNs, cards, health, location2TokenizeConsistent, format-preserving3Apply policyA rule per model, tool, role4LogEvery decision, recordedVector storeTokensLogsTokensBilling toolsCard, loggedPeople by roleUnmask by roleRisk assessment evidenceWhat each recipient received, and whosaw real values, for your assessment.Tokens onlyModel providers · their cloudAI models, any providerOpenAIAnthropicGooglexAIOr a model you host, such as OllamaSees tokens only. Answers come back with tokens,and Protecto restores real values by policy.
Real valuesTokensAnswers coming back
Three outcomes for every recipient
Tokenize

Default for models, stores and logs

529-41-7730 → [SSN_6c1]

The same customer always gets the same token, so the model can still follow the ticket.

Release

Real values where policy allows

billing tool ← card

A tool or role gets the real value its task needs, and the release is logged.

Hold back

Fields the task does not need

precise location → not sent

Data the task does not need stays out of the AI flow (Civ. Code 1798.100(c)).

Choose where Protecto runs

SaaS

Protecto’s managed service. The fastest way to put one workflow behind Protecto.

Your private cloud

Protecto runs in your own cloud account, next to your data.

On-premises or air-gapped

Your data center. Air-gapped runs with a model you host, with no outside connection.
Connect Protecto to your apps and agents

API or proxy

Call Protecto before the model, or route model traffic through Protecto.

MCP and tool calls

Protecto sits in the path of tool calls, so agents keep their workflows.

Start with one flow

One workflow, one sample of your records. Add flows as each assessment is done.
Your risk assessment

Six risk assessment fields, with evidence behind them.

The CCPA rules spell out what a risk assessment report must contain. Here is what changes in each field when Protecto sits in the AI data path.
  1. 01

    Purpose

    11 CCR 7152(a)(1)

    A specific purpose. The rules reject generic wording such as "to improve our services."

    With ProtectoOne flow per purpose, each with its own policy, so the purpose you write matches what runs.

  2. 02

    Minimum personal information

    11 CCR 7152(a)(2)

    The categories processed, including sensitive ones, and the minimum the purpose needs.

    With ProtectoThe model gets tokens in place of names, card numbers and health details. Fields the task does not need are held back.

  3. 03

    How the data moves

    11 CCR 7152(a)(3)

    How you collect, use, disclose and keep the data, and where it comes from.

    With ProtectoOne checkpoint to describe: each source, each recipient, and what each one receives.

  4. 04

    Negative impacts

    11 CCR 7152(a)(5)

    The harms to consumers, starting with unauthorized access or disclosure.

    With ProtectoA leaked vendor log or vector index holds tokens. The mapping stays apart from the model provider.

  5. 05

    Safeguards

    11 CCR 7152(a)(6)

    The rules give examples: encryption, segmentation, access controls and privacy-enhancing technologies.

    With ProtectoMasking before the model, unmasking by role and a policy per recipient, with logs that show them working.

  6. 06

    Updates

    11 CCR 7155(a)

    Update within 45 calendar days of a material change, and review at least every three years.

    With ProtectoWhen a team adds an agent or a data source, the logs show what changed in what the model receives.

Dates on the CCPA calendar
  1. Jan 1, 2026

    Regulations in effect. Assess new sensitive-data processing before it starts.

    11 CCR 7150, 7155(a)
  2. Jan 1, 2027

    Rules for automated decisionmaking in significant decisions apply.

    11 CCR 7200(b)
  3. Dec 31, 2027

    Deadline to assess processing that was already running before 2026.

    11 CCR 7155(b)
  4. Apr 1, 2028

    First risk assessment submission, attested by an executive. First audit reports for the largest businesses.

    11 CCR 7157, 7121
For your privacy team

Seven CCPA rules your AI workflow has to meet.

References are to the California Civil Code (CCPA, as amended by the CPRA) and the CCPA regulations in Title 11 of the California Code of Regulations, effective January 1, 2026.
RuleRequirementProtecto solution
Purpose and minimum dataCiv. Code 1798.100(c)Collection, use, retention and sharing of personal information must be reasonably necessary and proportionate to the purpose it was collected for.Each AI flow gets only the fields its task needs. The model reads tokens in place of names, card numbers and health details.
Reasonable securityCiv. Code 1798.100(e)
Civ. Code 1798.150
Keep reasonable security appropriate to the data. A breach of nonencrypted and nonredacted personal information can bring statutory damages of $107 to $799 per consumer per incident.Model inputs, vector stores and logs hold tokens. If one of them leaks, it does not hold the real card numbers or Social Security numbers.
Right to limit sensitive dataCiv. Code 1798.121
11 CCR 7027
Consumers can limit the use of sensitive personal information. Stop other uses within 15 business days and tell every service provider using it to do the same.Sensitive fields are tokenized by default, so fewer systems and vendors hold real values when a request to limit arrives.
Service providersCiv. Code 1798.100(d), 1798.140(ag)
11 CCR 7050
A written contract limits each service provider to the business purposes it names, and lets you stop and fix unauthorized use.Model providers receive tokens. The contract still matters, and far less real customer data sits under it.
Risk assessment11 CCR 7150, 7152
7155, 7157
Assess processing of sensitive personal information before it starts. Document the minimum data needed and the safeguards. An executive attests to the submission.Masking before the model, unmasking by role and per-recipient policy are safeguards you can name. Protecto's logs show them running.
Automated decisionmaking11 CCR 7200
7220 to 7222
From January 1, 2027, technology that makes significant decisions needs a pre-use notice, an opt-out or human appeal, and access rights.Protecto makes no decisions. Where AI supports a significant decision, Protecto's logs show which personal data reached the model and what was masked.
Cybersecurity audit11 CCR 7120 to 7124Businesses above the thresholds complete an annual independent audit that covers controls such as encryption and access controls. First reports are due from April 1, 2028.Tokenization, role-based unmasking and logs give auditors controls to test on the AI data path.

This page summarizes California law and regulations. It is not legal advice.
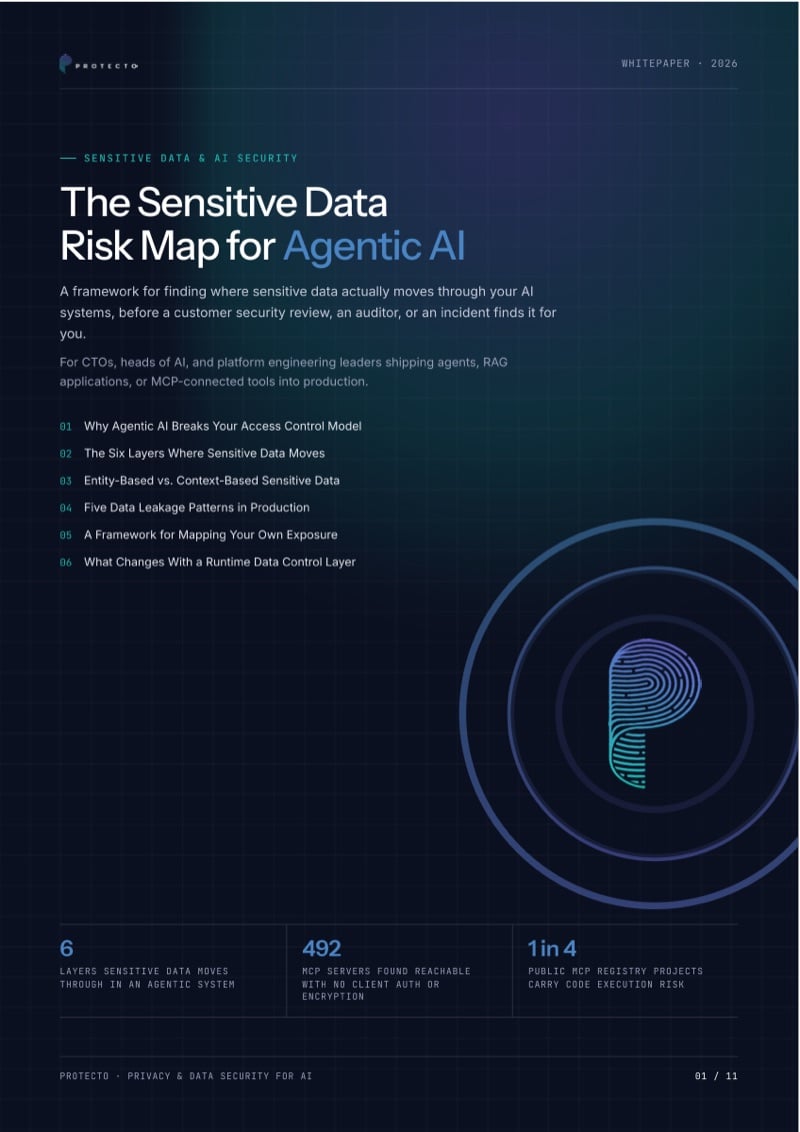
The risk map shows six layers where personal data moves in an AI system. Use it to scope your risk assessment.
Case study

How Automation Anywhere protects data for 5,000+ enterprise tenants.

AI and automation platform

Thousands of enterprise customers, each with its own rules for sensitive data.

Automation Anywhere runs Protecto Vault in a private cloud. Each tenant has its own protection policy and retention. Original values are revealed only to authorized users, and every reveal is logged.
5,000+
Live enterprise tenants
Policy
Set per tenant, with its own retention
Logged
Every reveal to an authorized user
Bring one AI workflow and a sample of your records. We will show what each recipient receives, and the log behind it.

More for your CCPA risk assessment.

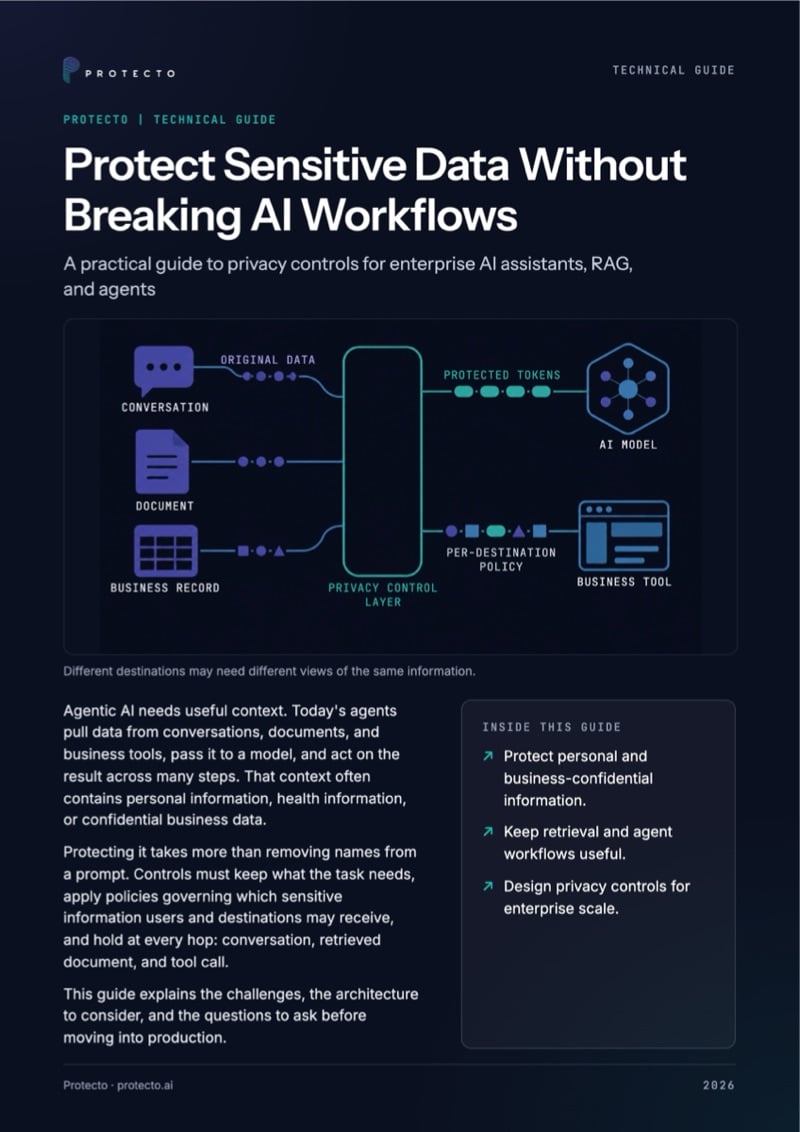
Cover Of The Guide Protect Sensitive Data Without Breaking Ai Workflows
Guide · 8 pages

Protect Sensitive Data Without Breaking AI Workflows

What the model, the tools and your people each need from the same customer record, and how to give each one only that.

Questions California privacy teams ask first.

Does the CCPA apply to AI systems?

Yes, whenever an AI system processes personal information about California residents. The statute says personal information can exist in AI systems that are capable of outputting it (Civ. Code 1798.140(v)(4)(C)). The usual duties on purpose, minimization and security apply to that data too.

Before processing that presents significant risk starts. The regulations list processing sensitive personal information, selling or sharing personal information, and using automated decisionmaking technology for a significant decision, among others (11 CCR 7150(b)). Processing that began before January 1, 2026 and continues must be assessed by December 31, 2027 (7155(b)).

Social Security, driver's license, state ID and passport numbers; account log-ins and card or account numbers with the code that unlocks them; precise geolocation; racial or ethnic origin, citizenship, religion and union membership; the contents of mail, email and texts; genetic, neural and biometric data; and health, sex life and sexual orientation data (Civ. Code 1798.140(ae)).

Not by default. Under the CCPA, "sharing" means disclosing personal information to a third party for cross-context behavioral advertising (1798.140(ah)). A provider that processes data for you under a written contract is usually a service provider, which comes with its own contract and use limits (1798.140(ag), 11 CCR 7050). How a given provider's terms fit is a question for your counsel.

Yes. Tokenization is pseudonymization: whoever holds the token mapping can reverse a token. The CCPA defines pseudonymized data as information that cannot be tied to a consumer without additional information kept separately (1798.140(aa)). Protecto keeps the mapping apart from the model provider, so the provider never holds the real values, but your CCPA duties still apply.

They apply if you use technology that replaces, or substantially replaces, human decisionmaking for a significant decision: lending and financial services, housing, education, employment or compensation, or healthcare services (11 CCR 7001(e), (ddd)). Advertising is not a significant decision. Businesses must comply from January 1, 2027, with a pre-use notice, an opt-out and access rights (7200 to 7222).

No. Consent and opt-out tools manage what you collect and what you tell consumers. DLP watches email, endpoints and the network. Protecto covers the AI data path, where personal information moves into models, vector stores, agent memory and tool calls, and works alongside both.

50+ entity types out of the box across PII, PHI and PCI, including names, Social Security numbers, card and account numbers, addresses and health details. You can add custom entities for identifiers specific to your business.

As Protecto's SaaS, in your private cloud, on your own servers, or air-gapped with a model you host. Protecto holds SOC 2 Type II and ISO 27001.
Bring one AI workflow. See what the model receives.

Use a sample of your own tickets or records. We will run Protecto on them and show the masking log your risk assessment can cite.
Cover of the whitepaper The Sensitive Data Risk Map for Agentic AI
Whitepaper

The Sensitive Data Risk Map for Agentic AI

A framework for finding where sensitive data moves through your AI systems, before a security review or an auditor finds it for you.

By submitting you agree to Protecto’s privacy policy.

Cover of the guide Protect Sensitive Data Without Breaking AI Workflows
Technical guide

Protect sensitive data without breaking AI workflows

A practical guide to privacy controls for AI assistants, RAG, and agents. One workflow traced from request to CRM update, with what each destination may see.

By submitting you agree to Protecto’s privacy policy.

Protecto Privacy Gateway for AI Chat is LIVE!
See how it works