Secure RAG in GPTGuard masks sensitive data before indexing and applies your access policy at retrieval. You skip building the RAG stack yourself.
SOC 2 Type II · ISO 27001 · HIPAA, BAA available
Which claims need a follow-up this week?
Found in claim-notes.pdfcall-log.docxsla-policy.pdf
Projected first-year savings at the insurer
Yearly US cost of the overbilling it targeted
Live enterprise tenants at Automation Anywhere
A company connects an assistant to its shared drive. An analyst asks a routine question, and the answer quotes a compensation file the analyst can’t open.
The permissions stayed on the file. They did not follow the chunks.
Once a document is chunked, embedded and retrieved, source rules often stop applying. RAG needs its own controls at retrieval.
Documents hold PII, PHI, contracts and pricing. Without protection, those values land in the index, the retrieved context and the response.
Ingestion, chunking, embedding, vector search, retrieval logic and agent APIs all come before the first secure answer.
Follow one claim note from upload to agent. In standard RAG, real values reach the model. In Secure RAG, everything after step 2 runs on tokens.
What your team does
You define who can see what. At retrieval, Protecto applies that policy for the user, the agent and the task.
The model reads tokens. Each reader sees the real values they are allowed to see, and the rest stay masked.
“What changes for the claims lead in March?”
A vector database covers part of one row. Secure RAG runs all six as one system, so your team can start on the agent.
| What secure RAG needs | If you build it | In Secure RAG |
|---|---|---|
| Document ingestion | Parsers, upload jobs and sync code for each source | Upload files, use the RAG Document API or sync SharePoint, deletions included |
| Sensitive data detection | Tune a detection model and maintain rules for your own IDs | 50+ entity types across PII, PHI and PCI, plus custom entities |
| Context-preserving masking | Redaction that removes what search and the model need | The same value always gets the same token, and the surrounding text stays |
| Indexing and retrieval | Chunking, embeddings and vector search, then tuning for masked text | Built in, with retrieval designed for protected content |
| Access control | Carry permissions onto every chunk and keep them current | Context-Based Access Control (CBAC), document categories and user groups |
| Audit and unmasking | Your own logging, approval and reveal workflow | Event logs for each data action, with real values revealed by role |
Your agent asks for context and gets masked passages back. It keeps its framework, its tools and its model.
Upload documents and retrieve relevant passages through the RAG Document API. Protecto also covers your agent’s MCP tool calls.
Protecto sits in front of the model. Use the provider you already have, and it receives masked context.
Run it as SaaS, on-prem, in a private cloud or air-gapped. Audit logs come with every option.
GPTGuard adds a secure chat interface on the same protected documents. Explore GPTGuard →
The team wanted LLMs to compare clinical notes with billing codes and flag overbilling. Every record held PHI.
Protecto scanned the clinical notes and masked PHI before they entered the pipeline.
The masked notes were vectorized and stored. LLMs ran similarity searches on them to flag billing discrepancies.
Fraud analysts reached original values through a secure unmask workflow when a case needed identifiable records.
“Protecto enabled us to deliver data security, privacy, and compliance for our AI features at scale across 5,000+ enterprise clients, strengthening customer trust in our AI automation solutions.”
A reference architecture, with a section on files, RAG and embedding inputs, and an evaluation checklist for your review.
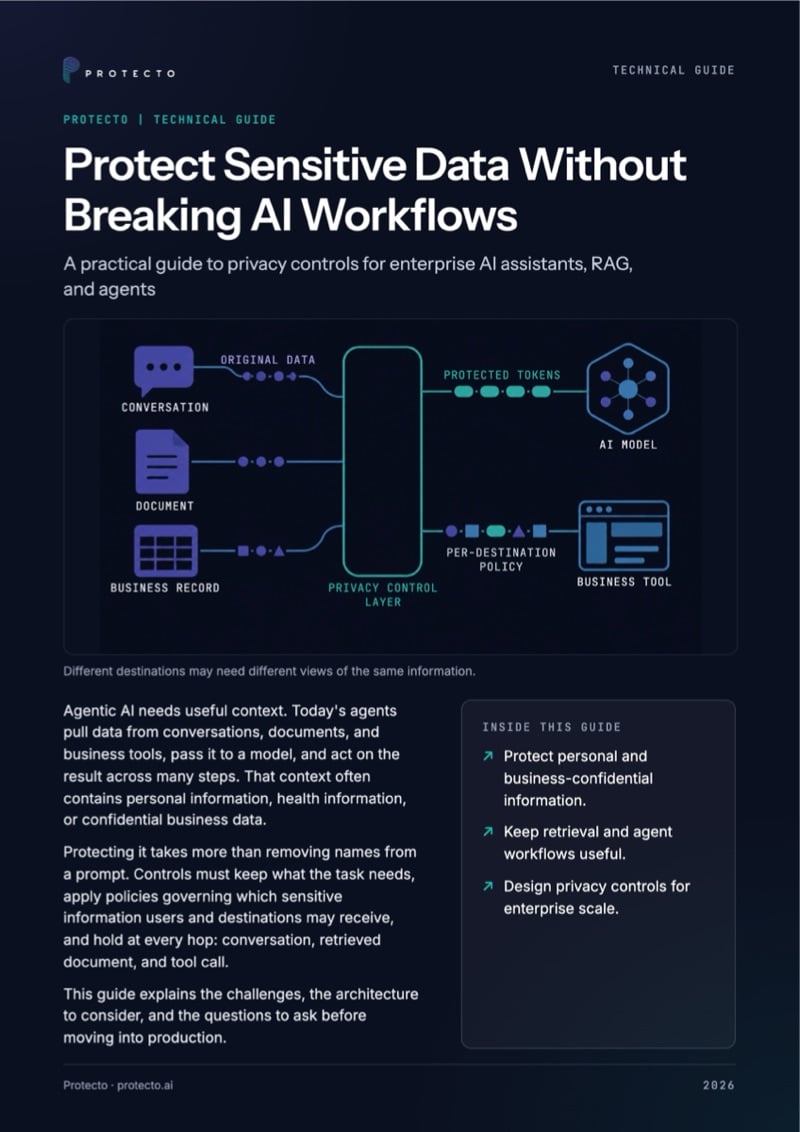
How to set a policy per destination for assistants, RAG and agents, with a checklist for production.
Four exposure surfaces and a five-question framework for checking where your AI data controls stand.
How Protecto protects documents at ingestion and applies policy at retrieval, so each reader gets the right view.
Secure RAG is retrieval augmented generation with data protection at each step. Sensitive data is masked before indexing, access policy applies at retrieval, and each action is logged. Standard RAG copies documents into an index, where source permissions often stop applying.
Secure RAG is the document retrieval layer in GPTGuard. Agents and applications use it through REST APIs. GPTGuard adds a secure chat interface for your staff on the same protected documents.
It can when placeholders carry no meaning. Protecto gives each value a consistent token and leaves the surrounding text in place, so search and the model still have the context they need. Retrieval is designed for protected content.
You define which documents, categories, entities and context each user or agent may see. Your application passes that context with an auth key, and Protecto applies it at retrieval. Restricted values stay masked for that reader.
Yes, by policy. Each person sees the real values they are allowed to see, and the rest stay masked. Each reveal is logged.
Yes. Protecto covers your agent’s MCP tool calls as well as the context it retrieves.
You can upload files, send documents through the RAG Document API or sync from SharePoint, including on-premises SharePoint. Deletions in SharePoint carry over, so removed files stop being searchable.
Yes. GPTGuard connects to Active Directory and Okta and supports SSO. When your own agent calls the API, your application passes each user’s role or identity with the request.
As SaaS, on-premises, in a private cloud or air-gapped. You can use any LLM provider. With on-premises or private cloud deployment, your documents are processed in your environment.
No. DLP keeps guarding the channels it covers. Secure RAG covers the documents and context flowing to your models and agents, and works alongside DLP.
Bring a sample, with test data if you prefer. In 30 minutes, we will show you what each reader and agent gets back.
A reference architecture for protecting sensitive data across agent workflows, for architects and AI platform engineers.
By submitting you agree to Protecto’s privacy policy.
A practical guide to privacy controls for AI assistants, RAG, and agents. One workflow traced from request to CRM update, with what each destination may see.
By submitting you agree to Protecto’s privacy policy.
What current industry research shows about where AI data controls fall behind adoption, with a five-question readiness framework.
By submitting you agree to Protecto’s privacy policy.