Data sovereignty for AI without giving up public models
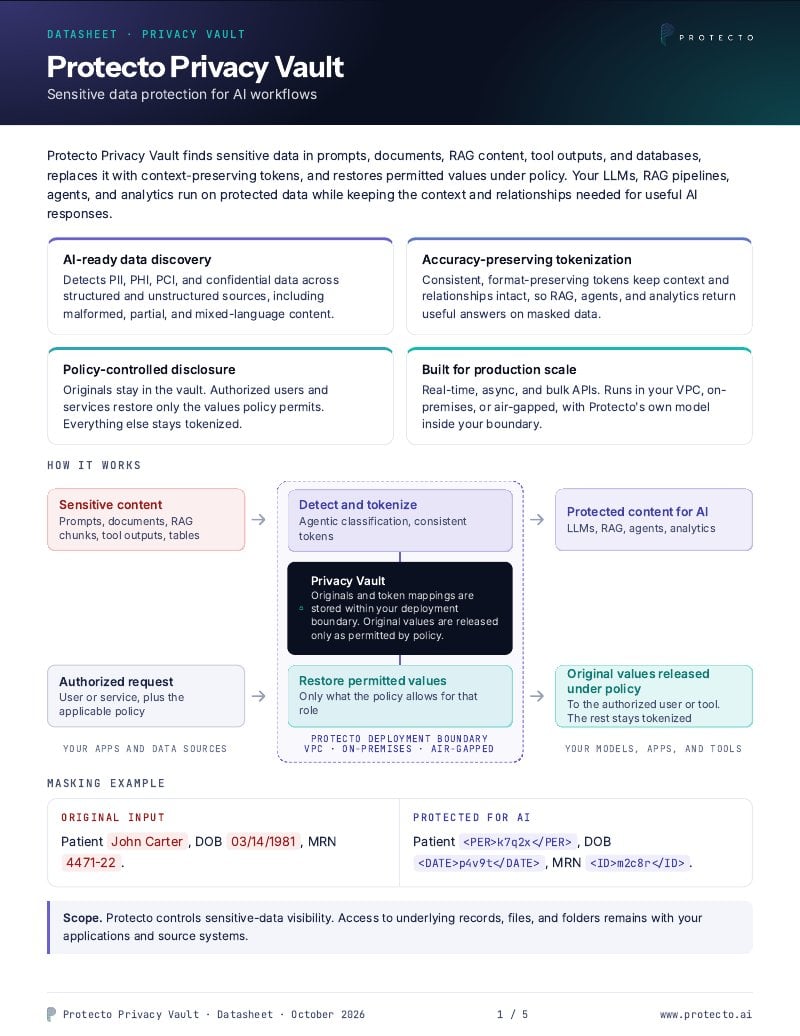
Protecto runs on-premises or in your private cloud and swaps sensitive values for tokens the AI can still use. Real values stay in your approved region or infrastructure.
A claims team at a European insurer builds an assistant on a public AI model. It reads the file, looks up the policy in the CRM and calls a tool to draft a letter. At each step, names, IDs and health details can reach a server in another country. The data protection officer asks where that data goes, and the launch waits.
This is the data sovereignty problem: the best AI runs somewhere your sensitive data may not be allowed to go.
Retrieved documents, tool and MCP calls, agent memory and answers can each carry sensitive data out of your region. A filter on the chat box covers one of those paths.
Local-only models cost you answers.
A smaller model hosted at home keeps the data there. Your teams give up model quality, and you pay to run and tune it.
Cutting the data out breaks the workflow.
DLP still guards email, endpoints and file transfers. Stopping AI traffic or redacting it to “[REDACTED]” leaves the model guessing, and the agent stops being useful.
What changes with Protecto in the path
Use leading public models
Send work to GPT, Gemini, Claude or a model you host. Real values stay in your approved infrastructure or region, and external models only receive tokens.
See and control where data goes
See where sensitive data flows, then decide which agents, models and tools receive it, as tokens or as real values.
Show how policy is enforced
Produce reports that show how your data policies were enforced, so a review starts from records instead of a diagram.
One integration point across agents, models and tools
Data passes through Protecto before it reaches a model, a search index or a tool. You add one control point, not a separate fix for each path.
Real timeProtects model input, retrieval, logs, tool calls and agent memory as data moves, not just stored files.
Real valuesTokensAnswers coming back
On-premises · Private cloud · Air-gapped · SaaS. When Protecto runs in your environment, token mappings, keys and logs stay on your servers.
Sovereign control of the data, with AI that still works
Protecto sits under your control and keeps the context a model needs to give a useful answer.
01
Runs under your control
Deploy on-premises or in your private cloud, air-gapped if you need it. Your team decides what leaves, and real values stay with you.
The same customer gets the same token in every message and document, and a tokenized IBAN still looks like an IBAN. Bank Muscat retained 85% semantic accuracy after masking.
How Bank Muscat kept customer data in the bank while adopting Gemini
Bank Muscat wanted Gemini for its teams, and customer data had to stay in the country. Its records mixed Arabic and English. Protecto ran in the bank’s Oracle Cloud environment, reached 99% recall and 96% precision, and got to a working proof in four weeks.
Transfers need a permitted purpose, adequate protection and only the minimum data. SAMA members should, in principle, use cloud services located in the Kingdom.
Summaries, not legal advice. Confirm your position with counsel.
Security & compliance
Built for regulated data at enterprise scale.
Protecto combines data protection, audit logs, and ready-to-use policies for regulated data, whether deployed as SaaS, on-prem, in a private cloud, or air-gapped.
SOC 2 Type II
Audited controls
ISO 27001
Certified ISMS
HIPAA
BAA available
GDPR
EU data ready
DPDP
India privacy law
CCPA / CPRA
US privacy
Independently verified to outperform AWS Comprehend and Microsoft Presidio · audit logs on every scan, mask, and unmask.
Go deeper on data sovereignty
Whitepaper · 14 pages
Data Protection Architecture for Agentic AI
A reference architecture for where data controls sit in agentic AI, from prompts to tool calls.
Can we use public models such as GPT, Gemini and Claude?
Yes. Protecto is model agnostic. External models receive tokens, and real values stay in your environment. You can also run a model you host behind the same policy.
What is the difference between data sovereignty and data residency?
Data residency is where data is physically stored. Data sovereignty is broader: it also covers which country's laws apply and who has legal authority to access the data.
Where can sensitive data leave my region in an AI workflow?
At any point where it reaches an outside service: prompts, documents retrieved for context, tool and MCP calls, agent-to-agent messages and responses. Protecto sits in each of these paths.
Do tokens still count as personal data?
Usually, yes. Tokenization is pseudonymization, not anonymization: while a mapping exists, a token can be linked back to a person. Your counsel decides what basis a path outside your region still needs. If your rules allow no outside path, host the model in your environment too.
Where do real values and token mappings live?
When Protecto runs in your environment, token mappings, keys and logs stay on your servers.
Does masking hurt the AI's answers?
Consistent, format-preserving tokens keep who-is-who intact, so the model can still reason over the file. Bank Muscat retained 85% semantic accuracy after masking, on mixed Arabic and English data.
How do we integrate Protecto?
Protecto is API-first. Your application calls Protecto before a model, retrieval or tool call, and again before the answer goes back. Bank Muscat reached a working proof of concept in four weeks.
Does detection work in our language?
Detection is officially tested in seven languages: English, German, French, Spanish, Dutch, Arabic and Japanese. Other languages are available on request and tested on your data.
What can we show a regulator or auditor?
Reports that show how your data policies were enforced, drawn from logs of what was found, what was masked and who saw real values.
Does Protecto replace DLP?
No. DLP keeps guarding email, endpoints and file transfers. Protecto covers where it falls short: AI traffic, context and unstructured data moving to models and agents.
See what leaves your region
Bring one AI project stuck on data sovereignty. We will show you what each model and tool receives.
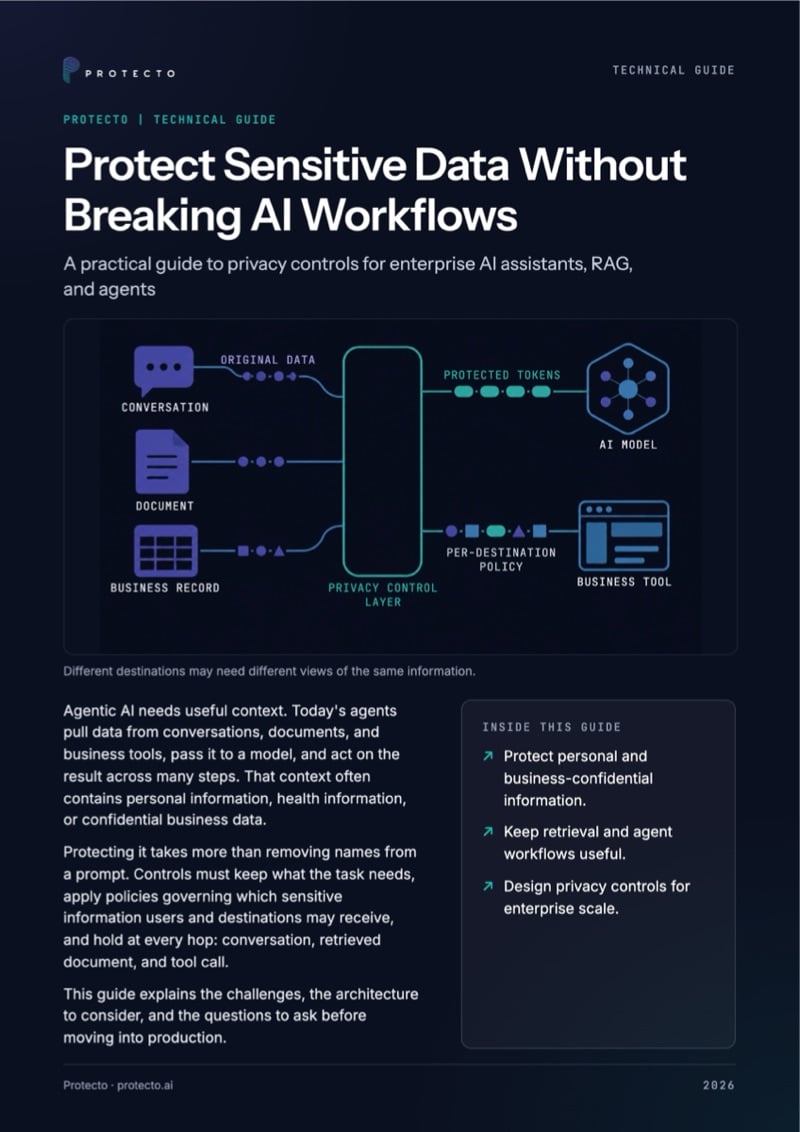
Protect sensitive data without breaking AI workflows
A practical guide to privacy controls for AI assistants, RAG, and agents. One workflow traced from request to CRM update, with what each destination may see.