Under HIPAA, health data is de-identified when it no longer identifies a person and there is no reasonable basis to believe it could. The Privacy Rule gives two ways to get there: Safe Harbor, which removes 18 types of identifiers, and Expert Determination, where a qualified expert documents that the risk of re-identification is very small. Once data is de-identified either way, it is no longer protected health information (PHI). For the general methods behind this, see our guide to data de-identification.
Here is what that means for one line of a discharge note:
Before
Maria Lopez (MRN 4471-0928) was admitted on 03/14/2026 to St. Anne's Hospital with heart failure. Her daughter Ana will drive her to follow-up.

After (Safe Harbor)
[NAME] (MRN [ID]) was admitted on [DATE] 2026 to [ORGANIZATION] with heart failure. Her daughter [NAME] will drive her to follow-up.
The diagnosis stays. The patient, her record number, the exact date, the hospital and her daughter’s name do not. Notice the daughter: Safe Harbor also covers identifiers of the patient’s relatives, employers and household members.
Key takeaways
- HIPAA has exactly two de-identification methods: Safe Harbor and Expert Determination.
- Safe Harbor needs all 18 identifier types removed, for the patient and for relatives, employers and household members, plus no actual knowledge that the rest could identify the person.
- Expert Determination keeps more detail, but needs a documented expert opinion.
- Clinical free text is where most Safe Harbor attempts fail. Identifiers sit inside sentences.
The Safe Harbor method

Safe Harbor has two conditions. First, remove the 18 identifiers below for the individual and for their relatives, employers and household members. Second, the organization must have no actual knowledge that the remaining information could identify the person.
The 18 HIPAA identifiers
- Names
- Geographic units smaller than a state, including street address, city, county and ZIP code
- All parts of dates related to the person, except the year (birth, admission, discharge and death dates), and all ages over 89
- Phone numbers
- Fax numbers
- Email addresses
- Social Security numbers
- Medical record numbers
- Health plan beneficiary numbers
- Account numbers
- Certificate and license numbers
- Vehicle identifiers and serial numbers, including license plates
- Device identifiers and serial numbers
- Web URLs
- IP addresses
- Biometric identifiers, such as fingerprints and voiceprints
- Full-face photos and comparable images
- Any other unique identifying number, characteristic or code
The ZIP code rule. You may keep the first three digits of a ZIP code only if the area those digits cover holds more than 20,000 people. Otherwise, replace them with 000.
Ages and dates. Keep the year, drop the day and month. Ages over 89 are grouped into one category, 90 or older.
The Expert Determination method
A person with knowledge of statistical and scientific methods for de-identification reviews the data and determines that the risk of identifying anyone is very small, both on its own and combined with other information the expected recipient could reasonably get. The expert documents the methods and the result, and the organization keeps that record.
Expert Determination is the better fit when the data must keep detail that Safe Harbor removes, such as exact dates for time-to-event studies or three-digit ZIP codes for regional analysis. Typical techniques include generalization, suppression of rare values, date shifting and pseudonymization.
Safe Harbor vs Expert Determination
| Safe Harbor | Expert Determination | |
|---|---|---|
| What it requires | Remove all 18 identifier types; no actual knowledge of identifiability | A documented expert opinion that re-identification risk is very small |
| Detail kept | Lower: dates reduced to years, locations to state | Higher: chosen to fit the use case |
| Cost and time | Lower; can be automated | Higher; needs an expert and a review |
| Best for | Repeatable releases, AI and analytics pipelines | Research that needs dates, locations or rare attributes |
Limited data sets are not de-identified
A limited data set removes direct identifiers but keeps some dates, city, state and ZIP code. It is still PHI. It can be shared for research, public health or health care operations only under a data use agreement.
Where Safe Harbor fails in practice
Removing a name column is easy. The failures happen in places column rules never check:
- Free text. Discharge summaries, progress notes and call transcripts mention names, dates, phone numbers and places in the middle of sentences.
- Other people. A daughter’s name, a spouse’s phone number or an employer in a note counts too.
- Dates written as words. “Admitted the Tuesday after Thanksgiving” is still a date.
- Rare facts. A rare condition in a small town can point to one patient, which counts as actual knowledge if you know about it.
For clinical notes sent to an LLM, read does redacting clinical notes meet HIPAA Safe Harbor? and is redaction enough for HIPAA when using ChatGPT or an LLM?
Is tokenized PHI still PHI?
Usually, yes. Tokenization is pseudonymization: while a mapping exists, a token can be linked back to a person. HIPAA does allow a covered entity to keep a re-identification code under specific conditions, but many teams keep their BAA and access controls in place for tokenized data. Your privacy team and counsel decide how each dataset is treated.
The upside of tokens is utility. When the same patient always gets the same token, joins across claims and notes, readmission counts and cohorts still work. Learn more about PHI de-identification for data lakes.
How to de-identify PHI for analytics and AI
- Pick the method per dataset. Safe Harbor for repeatable pipelines; Expert Determination when the use case needs more detail.
- Find identifiers in tables and free text. Include relatives, employers and household members, and your own identifiers such as member numbers.
- Choose the output. Tokens that approved roles can reverse by policy, or anonymization with no way back.
- Run it where the data moves. De-identify before data reaches the lake, the warehouse or the model, so raw copies do not spread.
- Measure what you missed. Test on a sample of your own notes and count missed identifiers before you rely on the output.
- Document and control access. Record the method, keep any mapping separate, and log who sees real values.
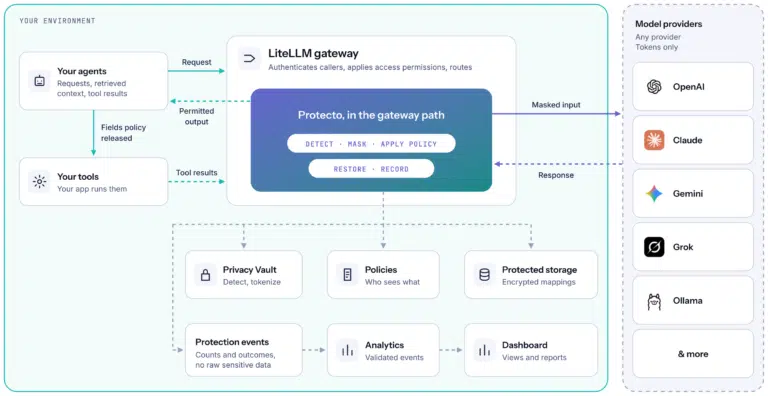
Protecto detects Safe Harbor identifiers in structured columns and in clinical free text, adds custom identifiers in days, and replaces them with consistent tokens or anonymizes them. Inovalon tested 1,000+ documents with Protecto in under a week. When Protecto hosts or manages the service, or has access to your installed instance, Protecto is a business associate and signs a BAA before PHI flows. When it runs in your environment with no Protecto access, Protecto does not receive PHI. For AI workflows where PHI has no fixed pattern, see how to de-identify PHI in AI workflows.
Frequently asked questions
Is de-identified data still covered by HIPAA?
No. Health information de-identified by Safe Harbor or Expert Determination is not PHI, so the Privacy Rule no longer limits its use or disclosure. Other laws, such as state privacy laws, may still apply.
What are the two HIPAA de-identification methods?
Safe Harbor, which removes 18 identifier types with no actual knowledge that the rest identifies anyone, and Expert Determination, where a qualified expert documents that re-identification risk is very small.
Do I need a BAA to share de-identified data?
No BAA is needed for data that is properly de-identified, because it is no longer PHI. Tokenized or limited data sets are different: they are usually still PHI. For LLM providers, see do you need a BAA to use ChatGPT with PHI?
Can de-identified health data be re-identified?
It can, if identifiers remain in free text or if the data is linked with other datasets. That is why Expert Determination looks at what a recipient could combine, and why testing on your own notes matters. More Privacy Rule questions are answered in de-identification under HIPAA: FAQ.
This post summarizes the HIPAA Privacy Rule. It is not legal advice. See also HIPAA compliance with Protecto.